Once a policy is live, Titan carries it straight into the audit cycle. Same platform, Same records, No handoff.
One platform to author, distribute, and enforce your policies and to plan, run, and close every audit against them. Titan runs both end to end, natively inside the Microsoft 365 you already have.
Centralize, version-control, and distribute all policies and SOPs with lifecycle workflows.
Plan, execute, and track internal audits against those policies. Close the compliance loop.
CAPA trending, management review dashboards. Drive systemic, organization-wide improvement.
Version Chaos
Multiple drafts circulate over email with no single source of truth. No one's sure which copy is current.
No Attestation Trail
Can't prove who actually read and acknowledged a policy, or when. Audit requests turn into a scavenger hunt.
Approval Bottlenecks
Sign-off chases stall in inboxes. Reviewers lose track of what's actually waiting on them.
Missed Renewals
Policies quietly go stale past their review date with nothing to flag it until an auditor does.
No Traceability
Audit findings scattered across Excel files. No link between finding, root cause, and corrective action.
Missed Deadlines
CAPA follow-ups rely on manual reminders. Overdue items slip through until the next external audit.
Audit Fatigue
Quality teams spend 40% of their time on admin, scheduling, chasing responses, compiling reports.
No Visibility
Management gets a static summary once a year. No real-time view of compliance status or NC trends.
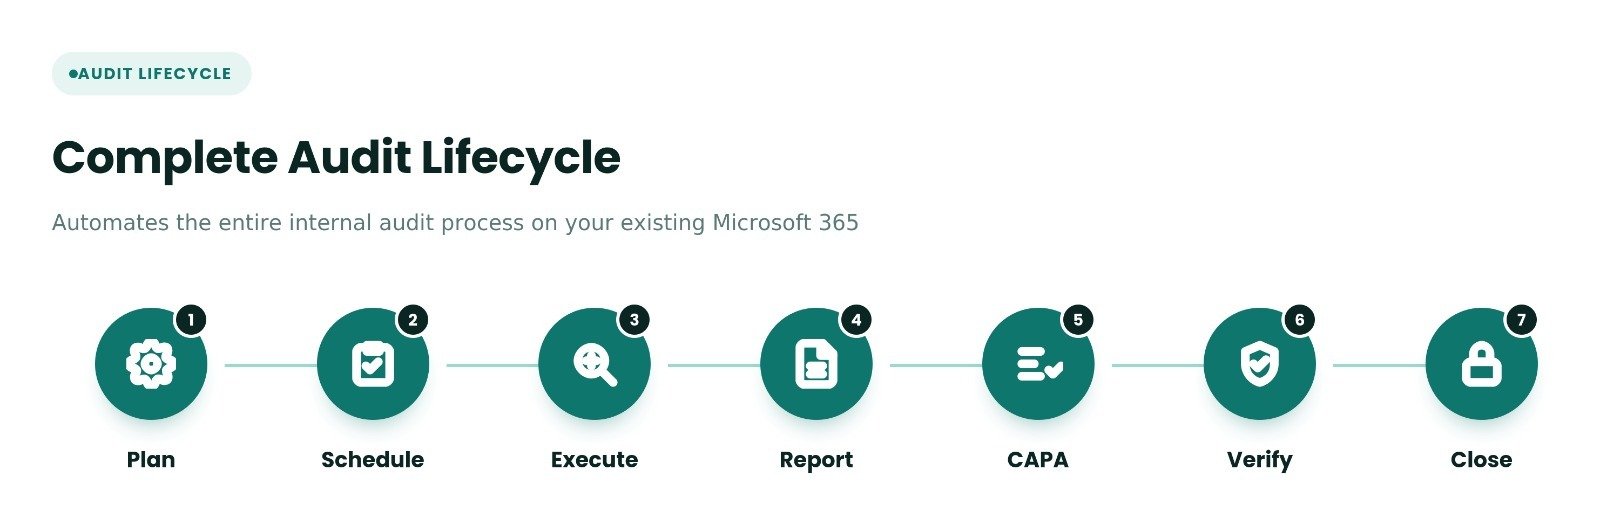
Titan doesn't stop at storing and versioning your policies and SOPs. It also runs your entire internal audit process end to end planning, scheduling, execution, findings, CAPA, verification, and closure, so governance and assurance live on one platform instead of two.
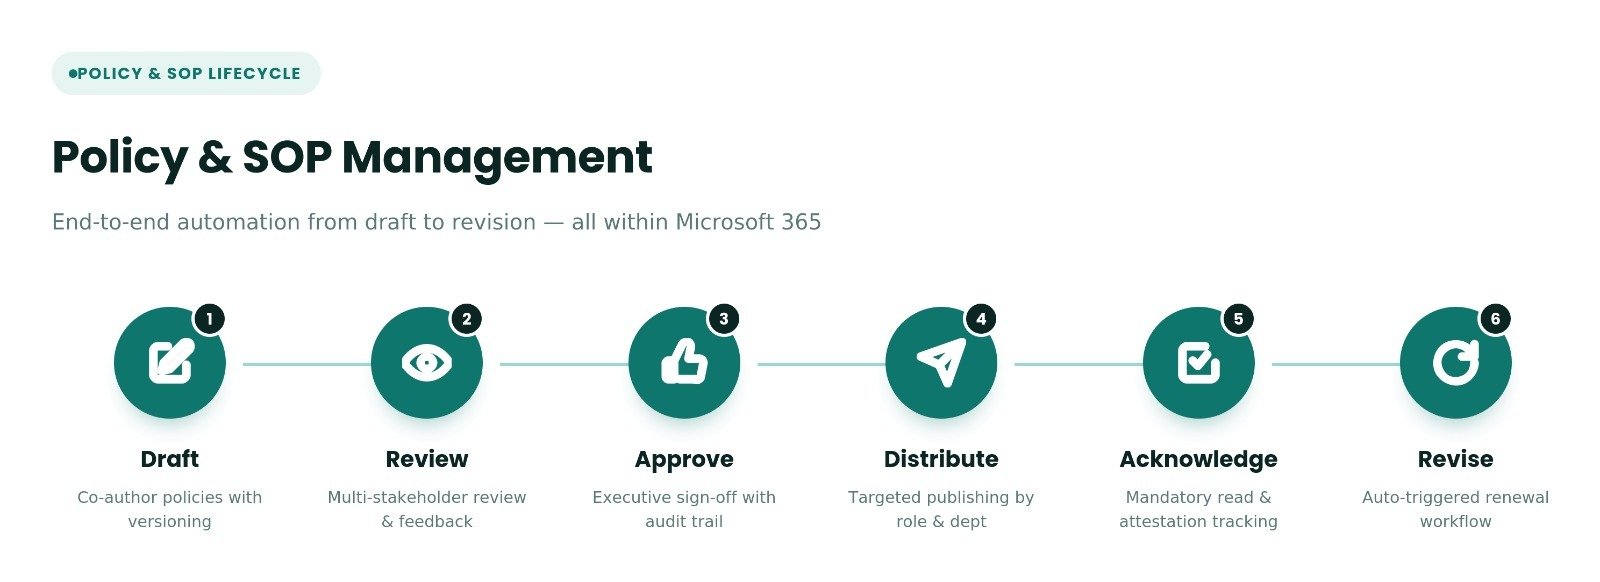
Centralize, version control, and distribute every policy with lifecycle workflows.
Plan, execute, and close internal audits against those same policies having nothing manual in between.
Once a policy is live, Titan carries it straight into the audit cycle. Same platform, Same records, No handoff.
Every draft, edit, and redline is preserved. Nothing gets overwritten silently — full history, always available.
Publish to exactly who needs it — filtered by role, department, or location — instead of one blast email to everyone.
Read receipts and e-signatures tied to each user, exportable as evidence the moment an auditor asks.
Review cycles fire automatically before a policy goes stale — nothing quietly expires unnoticed.
Every policy moves through a controlled, auditable path having co-authored, reviewed, signed off, published, attested to, and renewed automatically.
Every audit, finding, and CAPA gets a unique, traceable ID (AUD-YYYY-####).
Non-conformities automatically trigger corrective action workflows with assigned owners.
CAPAs cannot close without effectiveness verification. Audits cannot close with open NCs.
Automated emails at every step: assignment, reminders, escalations, and closures.
Mandatory selection: 5-Why, Fishbone, or custom. No CAPA closes without documented root cause.
Automated reminders at T-7, T-3, and due date. Overdue CAPAs escalate to Quality Head and Top Management.
Lead Auditor verifies corrective action worked. If not effective: CAPA reopens with a new due date.
Audit cannot close until every NC finding has a verified and effective CAPA. Zero loose ends.
Four purpose-built agents sit inside the same platform as your policies and audits, reading, writing, watching, and reasoning over your governance data so your team spends less time searching and more time deciding.
Ask a question in plain language and get the exact clause, SOP step, or policy version back instantly, with the source cited, instead of digging through folders.
Generates first drafts of policy and SOP updates from your inputs or regulatory changes, then tracks every revision, redline, and approval in a full version history.
Continuously watches obligations against actual practice, flags drift or emerging gaps in real time, and surfaces a live compliance status instead of a point-in-time snapshot.
Reads findings and CAPA data across audits to surface root cause patterns, recurring NCs, and department level risk trends, revealing insights that a manual annual review may miss.
Drag-and-drop workflow builder. Change processes without IT intervention or vendor change requests.
Policy management + audit management + CAPA on one platform. No integration headaches.
Runs entirely inside your Microsoft 365. SharePoint, Power Automate, Azure AD on tools you already own.
Auto ID generation, auto CAPA triggers, auto notifications, auto escalations. Less admin, more auditing.
Real-time dashboards for management review. No more waiting for the annual quality report.
Already deployed in various industries and quality environments. Battle tested workflows.
| Area | Today (Manual) | With Titan IAMS |
|---|---|---|
| Audit scheduling | Excel + email, 2–3 days | One-click, 30 minutes |
| Finding traceability | Scattered across files | Auto linked Audit → NC → CAPA |
| CAPA follow-up | Manual reminders, often missed | Auto-escalation, zero misses |
| Management reporting | Annual static summary | Real time dashboards |
| External audit prep | 2–4 weeks scramble | Always audit ready |
Policies live in SharePoint. Notifications reach users through Teams and Outlook.
Leverages your existing identity, groups, Conditional Access, and permissions.
Works with retention labels and records management for defensible compliance.
Extend workflows with no-code automation for custom business processes.
Runs inside Government Community Cloud for federal & public sector orgs.
Inherits encryption at rest/in transit, DLP, and your compliance controls.